Rose debug info
---------------

Human Factor Blog

how human behavior affects security

Programmer’s Digest #205

09/30/2026-10/07/2026 Critical Atlassian Flaw; WordPress Malware Comes Back After Removal; GitLab Patches Critical AI Gateway Flaw And More.

1. Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products

A critical flaw (CVE-2026-21589, CVSS 9.3) in eight self-hosted Atlassian Data Center products lets unauthenticated attackers read files in the web application root directory. Attackers must already know a file’s exact name and path. Atlassian disclosed it on October 5 and listed fixed versions per product. Cloud products are already patched.

Atlassian advises upgrading to a fixed LTS version or later, including for end-of-life releases. If that isn’t possible immediately, take the instance offline or restrict external access. Temporary mitigations block URLs with “..” next to “/”, “” or “::”, including encoded forms, via a WAF or reverse proxy, a Tomcat RewriteValve rule, or urlrewrite.xml (Bitbucket). Atlassian calls these limited and no replacement for patching.

Details are inconsistent: the Crowd and Bamboo fixed versions differ between the advisory and the CVE record. Server editions are listed as affected with no fixes.
Atlassian found no exploitation in cloud, but can’t confirm for self-hosted instances. Teams should search access logs for traversal patterns. A similar Jira flaw (CVE-2021-26086) was later exploited.

2. WordPress Malware Comes Back After Removal Using a Self-Healing Backdoor

A WordPress backdoor called SC, documented by Sucuri on September 30, 2026, restores deleted malware within seconds by spreading its components across website files, the database, and server memory. The report doesn’t establish the original entry point or how many sites are affected.

SC occupies at least eight locations. A configuration directive launches a loader before ordinary PHP requests, and the loader rebuilds a fake caching plugin from copies, encoded backups, or recovery archives. Early-loading components and an injected theme block provide further recovery routes. The backdoor hides from plugin lists and update checks, conceals an administrator account, and can forge authentication cookies. For commands, it queries smart contracts through about twenty public Ethereum gateways, so blocking one route doesn’t help. Replies can deliver PHP, browser scripts, or orders to delete security plugins.

Sucuri advises neutralizing the loader target first, then removing the directive. Next come database payloads, shared memory copies, scheduled tasks, triggers, and hidden admins, then all files in one pass. Finish by closing the entry point and rotating credentials.

3. LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings

Researchers have shown that a malicious spreadsheet can make LibreOffice and Apache OpenOffice run attacker code the moment it’s opened, with no macro-style warning. It works only when Java support is enabled, and so far exists only as a proof of concept, with no reported real-world use.

The attack chains normal features: a spreadsheet’s auto-refreshing “database range” fetches an ODB file from a web address, which names a JDBC driver hosted in a remote JAR file. The program downloads and starts it, running the attacker’s code without ever asking the user to trust the document. Researchers tested it on Windows and Linux.

LibreOffice fixed CVE-2026-63277 on October 5; users should update to 26.2.5 or 26.8.0. Apache OpenOffice (CVE-2026-59265) remains unpatched through version 4.1.16, with a fix expected in 4.1.17. Until then, disable Java or avoid opening untrusted spreadsheets.

4. GitLab Patches Critical AI Gateway Flaw Allowing Arbitrary Command Execution

GitLab has patched CVE-2026-90970 (CVSS 9.9), a critical flaw in its AI Gateway that lets authenticated users run arbitrary commands on self-hosted deployments. It affects versions from 18.1.6 up to, but excluding, 19.2.4, plus the 19.3 branch before 19.3.2 and the 19.4 branch before 19.4.1.

The bug is an improper neutralization issue in the custom-flow prompt template mechanism. A user with Duo Agent Platform access can submit a crafted flow configuration, escape the template sandbox, and execute commands on the gateway host or container.

Fixed releases are 19.2.4, 19.3.2, and 19.4.1. GitLab lists no workaround, so upgrading is the main mitigation. Because the AI Gateway is separate from the core application, administrators should check the gateway image or Helm configuration rather than assume a GitLab CE/EE upgrade covers it. Teams should also restrict flow-configuration access and review recent templates for unexpected changes.
GitLab.com, Dedicated, and instances using a GitLab-hosted gateway need no action.

5. 100+ Compromised Websites Use Fake Cloudflare Checks to Deliver LunexStealer

CERT-UA has identified over 100 websites compromised in September 2026 with malicious JavaScript that serves LunexStealer, a campaign attributed to the cluster UAC-0277. Visitors see a fake Cloudflare verification page that tricks them into running a command (ClickFix), which installs a malicious MSI package. The script retrieves its settings from a Polygon or Ethereum smart contract (EtherHiding), and the lure is shown only to Windows users arriving from search results.

Three MSI variants exist: a basic installer; one that bypasses UAC, sets Defender exclusions and abuses a vulnerable AMD driver to blind security tools; and one that uses DLL sideloading.

LunexStealer also installs a browser extension, LUNARAXE, posing as “Microsoft Office Word Editor”. It steals cookies, history and credentials, strips CSP headers and can run arbitrary JavaScript. The NAIVEMESS component gives it file system access.
CERT-UA advises blocking the Run dialog, restricting MSI installs, monitoring msiexec.exe, enabling Microsoft’s vulnerable driver blocklist, and allowlisting browser extensions.
13 h   digest   programmers'

Programmer’s Digest #204

09/23/2026-09/30/2026 MCP Python SDK OAuth Flaw; Malware Spread Through Terraform Providers; AI-Powered CARBONATO Botnet Steals Credentials And More.

1. MCP Python SDK OAuth Flaw Lets Malicious Servers Steal Credentials and Take Over Accounts

A high-severity OAuth flaw in Anthropic’s official MCP Python SDK lets a malicious MCP server steal authentication material and take over accounts. Cycode says it affects HTTP-based clients on SDK versions 1.9.1 through 2.1.1.

The bug lies in OAuth discovery. An attacker-controlled server returns a 404 during authorization-server discovery, pushing the SDK onto a fallback path that accepts server-supplied OAuth metadata without validating the issuer. The metadata can name a legitimate provider, such as Okta, Google or Microsoft Entra ID, while pointing to an attacker’s token endpoint.

The victim still sees a real login page. Afterward, the client sends the authorization code, client secret and PKCE code_verifier to the attacker, who can redeem the code for a valid access token. Stolen secrets and refresh tokens may grant persistent access to cloud services and internal APIs.

Servers, local stdio clients and clients using their own tokens are unaffected. Upgrade to 1.30.0 or 2.2.0, clear stored registrations, and rotate secrets and revoke tokens if a client may have contacted an untrusted server. Also set issuer= explicitly for ClientCredentialsOAuthProvider and PrivateKeyJWTOAuthProvider.

2. The Malware Hiding in Developer Tools That Turned Terraform Providers Into Attack Paths 

Malware has reached the tools developers use to manage cloud infrastructure. A campaign linked to Graphalgo planted a remote access program in Terraform providers and Go packages. It is the first time the firm has seen malware spread through Terraform providers.

In early September, attackers published two providers, one a typosquat of a popular Docker provider with 56 million downloads. The hidden code activates only when two Terraform inputs produce a specific hash, which makes casual testing unlikely to expose it. Two Go modules carried similar payloads, one hiding its code in an archive posing as a database file.

Once active, the malware reports system details via Slack and takes commands through Slack or an Ethereum test-network smart contract. Operators can run more Go or JavaScript code, or wipe the malware. Researchers counted 18 hostnames checking in: three Windows, five Linux and 10 Macs.

Affected teams should isolate the host, rotate credentials (cloud ones first), review recent Terraform runs and builds, and reimage. Preserve logs before cleanup.

3. Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

The placeholder domain “third-party[.]com” has been serving a ClickFix lure to Windows browsers while showing a harmless decoy to other users. Unlike example.com, the domain is not IANA-reserved, so someone registered it. It is now flagged as malicious on VirusTotal and Google Safe Browsing. Since at least June 2026, Windows visitors have seen a fake Cloudflare check that poisons the clipboard and tells them to paste a command into the Run dialog, which fetches a remote PowerShell payload. macOS users see an error saying only Windows is supported. The domain appears in over 1,700 GitHub repositories, including AI agent skills and MCP-server docs.

Manifold found 13 more non-reserved placeholder domains. Two, yoursite[.]com and your-domain[.]com, serve scams and scareware to macOS users. Because the payload depends on the visitor, static file scans miss it. Developers should audit their docs and tests and use only reserved placeholders such as example.com, .org and .net.

4. AI-Powered CARBONATO Botnet Steals Credentials to Fund Its Own LLM Gateway

CARBONATO is a Docker-based botnet, active since at least October 2024, that ThreatDown uncovered after finding the attackers’ unauthenticated container registry exposed online. In one day of passive collection, researchers pulled 4.3 GB of image data covering 59 repositories, 234 tags and 605 file blobs. The image histories revealed command-and-control addresses, bot tokens and the shared password for the crew’s own AI gateway. Evidence, including UTC-06:00 timestamps, the Telegram handle “Carbo506” and Costa Rican network infrastructure, points to Costa Rica.

The bot scans for Docker daemons that accept unauthenticated connections on port 2375. It then uses the Docker API to launch a privileged container with the host filesystem mounted and runs commands on the underlying machine. The container opens a reverse SSH tunnel to a relay in Costa Rica, using a port derived from the MD5 hash of the victim’s IP, installs an SSH server with the crew’s key, and sends a deployment report to Telegram.

Afterward, the implant installs the open-source Hermes Agent, whose persona file is rewritten to prioritize stealing AI API keys, and the botnet keeps spreading across networks on its own.

5. New Spectre-v2 BTR Attack Leaks Linux Memory Despite Existing Defenses

Researchers from VUSec and Scuola Superiore Sant’Anna have disclosed Branch Target Reuse (BTR), a new Spectre v2 variant that targets Just-In-Time (JIT) engines in browsers, language runtimes and operating system kernels across multiple CPU vendors. Modern CPUs restore code coherence after self-modification but don’t necessarily invalidate stale indirect branch predictions. When a JIT engine frees code and later reuses the address, an attacker can trigger a speculative jump to the obsolete entry point, hijacking control flow and leaking data.

BTR affects SpiderMonkey (Firefox), GraalVM and the Linux kernel’s cBPF JIT. Two proof-of-concept exploits recovered the root password hash within minutes on a fully patched Intel system with default protections. The attack also undermines mitigations for Training Solo (CVE-2024-28956 and CVE-2025-24495).

Linux has merged fixes (CVE-2026-64507 and CVE-2026-64508). GraalVM now randomizes JIT code-cache locations, while Mozilla is prioritizing site isolation over IBPB-based mitigations. The researchers warn that similar CPU flaws in handling rewritten code may emerge.

8 d   digest   programmers'

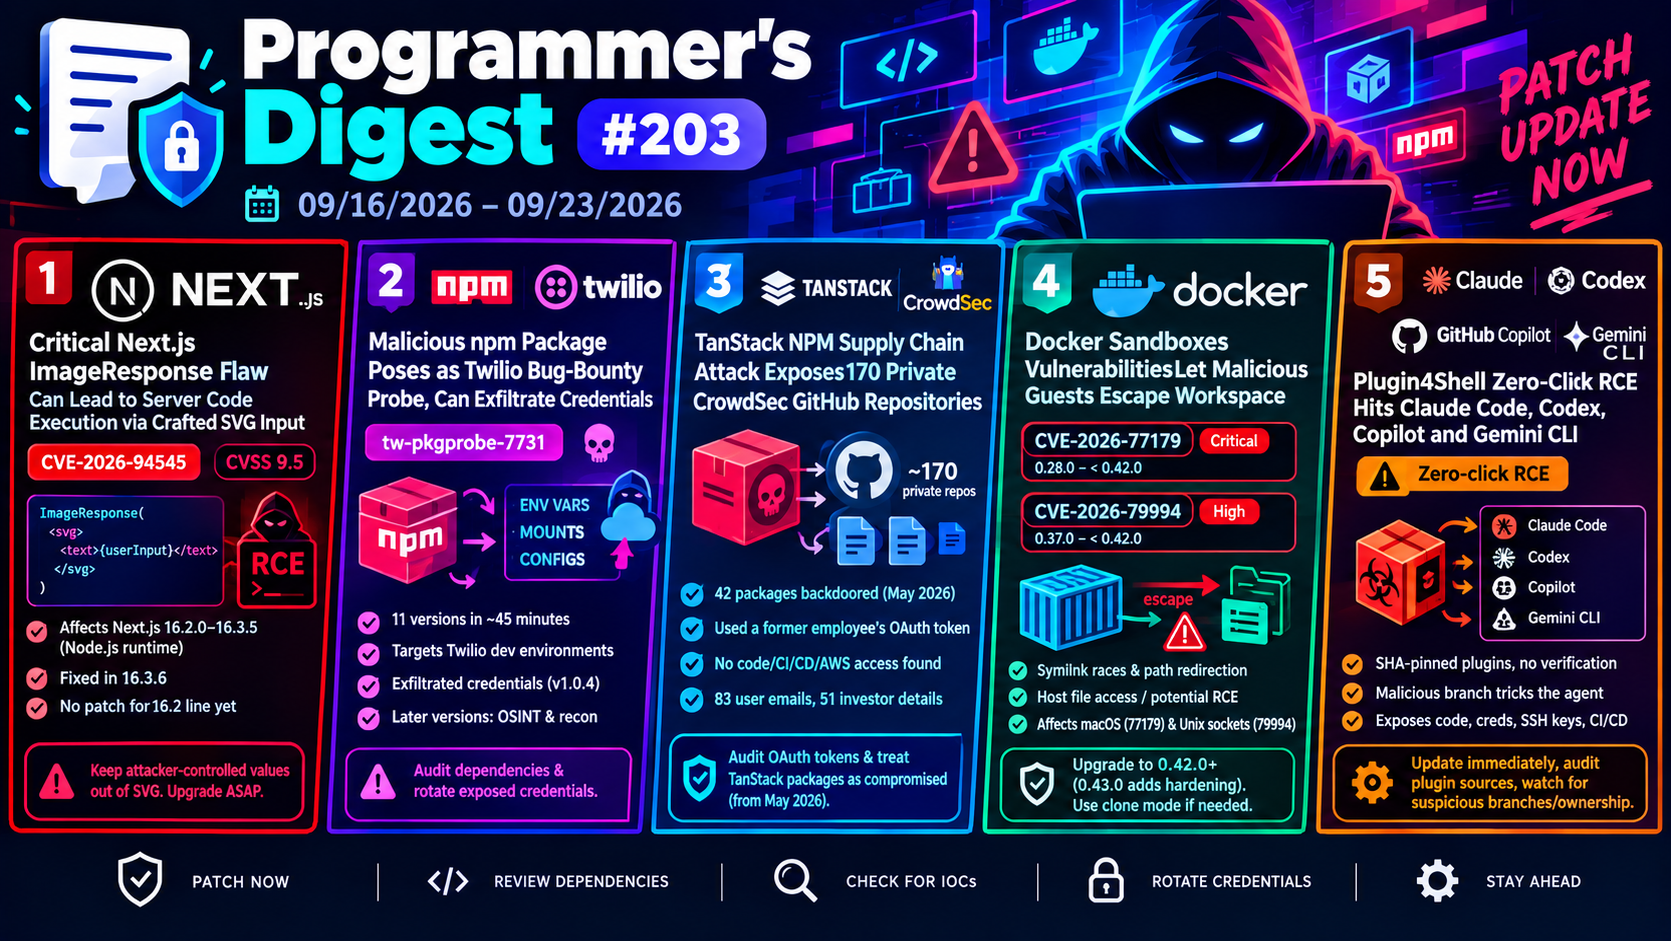
Programmer’s Digest #203

09/16/2026-09/23/2026 Critical Next.js ImageResponse Flaw; Malicious npm Package Poses as Twilio Bug-Bounty Probe; Docker Sandboxes Vulnerabilities And More.

1. Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input

A critical Next.js flaw (CVE-2026-94545, CVSS 9.5) in ImageResponse – used for Open Graph/social preview images – can let attackers run code on the server. It hits apps that pass attacker-controlled values (e. g., request URL text) into SVG content, attributes, or styles during image generation, since ImageResponse builds images via Vercel’s Satori library, which failed to properly escape such values.

Affected: Next.js 16.2.0–16.3.5 on the Node.js runtime (default); the Edge runtime and Next.js 15 are unaffected. Fixed in 16.3.6 (npm install [email protected]); no patch exists yet for the 16.2 line. Next.js 15.5.26 adds hardening to next/og. If upgrading isn’t possible, keep attacker-controlled values out of SVG rendered by ImageResponse.

To check exposure, look for ImageResponse imported from next/og in route handlers and opengraph-image files. No public exploits or attacks were reported as of September 23. Satori itself is fixed in 0.33.5 for direct users.

2. Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials

A malicious npm package, “tw-pkgprobe-7731,” posed as an authorized Twilio bug-bounty research tool while harvesting sensitive data. Published in 11 versions over ~45 minutes in mid-August 2026 by the now-deleted account “twdepprobe7731,” it only activates inside Twilio developer environments, then exfiltrates env variables, mounts, and configs via webhook.

Later versions (1.0.1–1.0.3) targeted specific Twilio account SIDs and injected a PoC package into node_modules when matches were found. Version 1.0.4 added theft of ACCOUNT_SID and AUTH_TOKEN, compromising Twilio credentials outright. The final three versions reverted to basic, non-malicious probing but added OSINT scanning of internal Twilio hosts and AWS metadata endpoints.

ReversingLabs says the package violated Twilio’s HackerOne guidelines, and the lack of obfuscation or typosquatting suggests a less sophisticated actor. Developers integrating Twilio should audit dependencies for this package and rotate any exposed credentials.

3. TanStack NPM Supply Chain Attack Exposes 170 Private CrowdSec GitHub Repositories

CrowdSec disclosed that the May 2026 TanStack npm supply-chain attack (42 packages backdoored with Shai Hulud malware by TeamPCP/UNC6780) led to attackers cloning ~170 private CrowdSec GitHub repos on May 22, using a GitHub OAuth token from a former employee’s account that had been left active post-departure. The attacker published the archive on a breach forum September 16, including private code, SaaS components, and internal tooling.

No evidence of code changes, CI/CD tampering, or AWS infrastructure access was found. One exposed AWS SNS credential was narrowly scoped and tested but not exploited further. The leak also exposed 83 user emails (<0.05% of users) and details on 51 potential investors from 2020.

CrowdSec is deploying EDR on developer workstations and tightening GitHub monitoring, credential review, and offboarding. Developers should audit OAuth tokens for departed employees and treat TanStack packages from that period as compromised.

4. Docker Sandboxes Vulnerabilities Let Malicious Guests Escape Workspace and Access Host Files 

Two Docker Sandboxes vulnerabilities let malicious guest code escape workspace isolation via symlink races—altering a validated path before the host acts on it. CVE-2026-77179 (Critical, versions 0.28.0–before 0.42.0) affects macOS’s virtio-fs host server, letting a compromised sandbox replace a directory with a symlink to read/write arbitrary host files as the VMM user, potentially leading to host code execution. CVE-2026-79994 (High, 0.37.0–before 0.42.0) affects the guest-to-host Unix socket relay, allowing redirection to unauthorized AF_UNIX sockets and potential data disclosure or access to privileged local IPC services.

Both stem from treating pathname validation as one-time rather than re-checked at use. This is especially relevant for AI-agent and dev workflows handling untrusted repos or dependencies.

Fix: upgrade to Docker Sandboxes 0.42.0+ (0.43.0 adds further hardening). If not possible, use clone mode and avoid read-write host mounts.

5. Plugin4Shell Zero-Click RCE Hits Claude Code, Codex, Copilot and Gemini CLI

Plugin4Shell is a zero-click RCE flaw affecting Claude Code, Codex, GitHub Copilot, and Gemini CLI, exploiting how these agents handle SHA-pinned plugin versions. Agents check out a pinned commit but never verify the working tree matches it. Attackers can create a Git branch named after the commit hash (or, for Gemini CLI, named “FETCH_HEAD”), tricking the agent into checking out malicious code while reporting a successful, “verified” install.

Because Claude Code and Codex auto-update plugins by default, no user action is needed—attackers can compromise a trusted plugin’s upstream repo after adoption. Given plugins inherit the developer’s permissions, exploitation can expose source code, cloud credentials, SSH keys, and CI/CD secrets.

Status: Fixed in Claude Code 2.1.179 and Codex 0.146.0. Gemini CLI won’t be patched (deprecated; migrate to Antigravity). Copilot remains unpatched, though GitHub blocks SHA-like branch names—self-hosted/Bitbucket marketplaces may still be exploitable. Action: update immediately, audit plugin sources, and watch for unexpected branch/ownership changes.

14 d   digest   programmers'
Earlier Ctrl + ↓